Introduction
In today’s highly connected world, keeping your network safe from cyber threats is more important than ever. Whether you are a cybersecurity enthusiast, a student, or an IT professional, understanding how to monitor your network for malicious activity is a must-have skill.
In this blog, I am going to walk you through my project: Building a Network Intrusion Detection System (NIDS) using Suricata IDS and Wazuh SIEM.
By the end of this guide, you will have a working setup that detects suspicious network traffic (like Nmap scans) and instantly reports it to a beautiful security dashboard.
You can find the complete project files and documentation in my GitHub repository here:
👉 Network Intrusion Detection using Suricata & Wazuh
What are Suricata and Wazuh?
- Suricata is a high-performance, open-source Network Threat Detection and Intrusion Detection System (IDS/IPS). Think of it as a vigilant security guard monitoring network traffic for known signatures, malicious patterns, and anomalous protocol behaviors.
- Wazuh is a free, open-source Security Information and Event Management (SIEM) and XDR platform. It acts as the central brain—collecting logs from agents and network sensors like Suricata, analyzing and correlating them through detection rules, and presenting actionable threat intelligence in an easy-to-read dashboard.
Architecture Overview
Attacker Machine (Reconnaissance / Nmap Scan)
                     |
                     | Raw Network Packets
                     v
             Monitored Target / Sensor
  +-----------------------------------------------+
  |  Suricata IDS (Engine)                        |
  |    -> Inspects packets against rule signatures |
  |    -> Generates alert log:                    |
  |       /var/log/suricata/eve.json              |
  |                                               |
  |  Wazuh Agent                                  |
  |    -> Reads eve.json via <localfile>          |
  |    -> Ships alerts via encrypted TCP (1514)   |
  +-----------------------------------------------+
                     |
                     v
             Wazuh Manager (SIEM)
  +-----------------------------------------------+
  |  analysisd Rule Engine                        |
  |    -> Matches custom rules (local_rules.xml)   |
  |    -> Escalate Nmap scans (Rule 100200 / 100600) |
  +-----------------------------------------------+
                     |
                     v
             Wazuh Dashboard
  +-----------------------------------------------+
  |  SOC Analyst Triage & Forensic Details         |
  |  (Source IP, Target Port, Triggered Signature) |
  +-----------------------------------------------+
Step 1: Forwarding Suricata Logs from the Wazuh Agent
Once Suricata is installed on your target machine, it writes its alerts to a log file (usually eve.json and fast.log). We need to instruct the Wazuh Agent to ingest this file and forward it to the Wazuh Manager.
Open the Wazuh Agent configuration file on your monitored machine:
sudo nano /var/ossec/etc/ossec.configAdd the following configuration block inside the <ossec_config> section to monitor the Suricata JSON and fast logs:
<!-- ADD SURICATA LOG MONITORING -->
<localfile>
  <log_format>json</log_format>
  <location>/var/log/suricata/eve.json</location>
</localfile>

<localfile>
  <log_format>json</log_format>
  <location>/var/log/suricata/fast.log</location>
</localfile>
Save the file, and then restart the Wazuh Agent service to apply the changes:
sudo systemctl restart wazuh-agent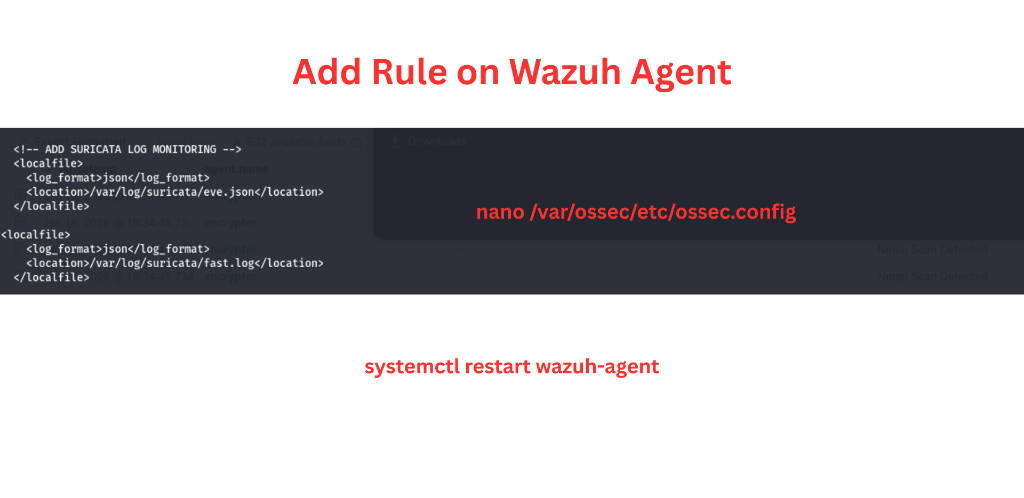
Step 2: Adding Custom Rules to the Wazuh Manager
Now that the agent is sending logs, the Wazuh Manager needs custom detection logic to properly identify and escalate specific attacks, such as an Nmap reconnaissance scan.
On your Wazuh Manager server, open the local rules configuration file:
sudo nano /var/ossec/etc/rules/local_rules.xmlAdd the following custom rule to detect Nmap scans identified by Suricata:
<!-- Suricata: Nmap scan detection -->
<rule id="100200" level="12">
  <if_group>suricata</if_group>
  <field name="alert.signature">^ET SCAN.*Nmap</field>
  <description>Nmap scan detected by Suricata: $(alert.signature)</description>
  <group>attack,network_scan,mitre_t1046</group>
</rule>
Make sure the manager's configuration is also set up to parse the incoming logs, then restart the Wazuh Manager service:
sudo systemctl restart wazuh-manager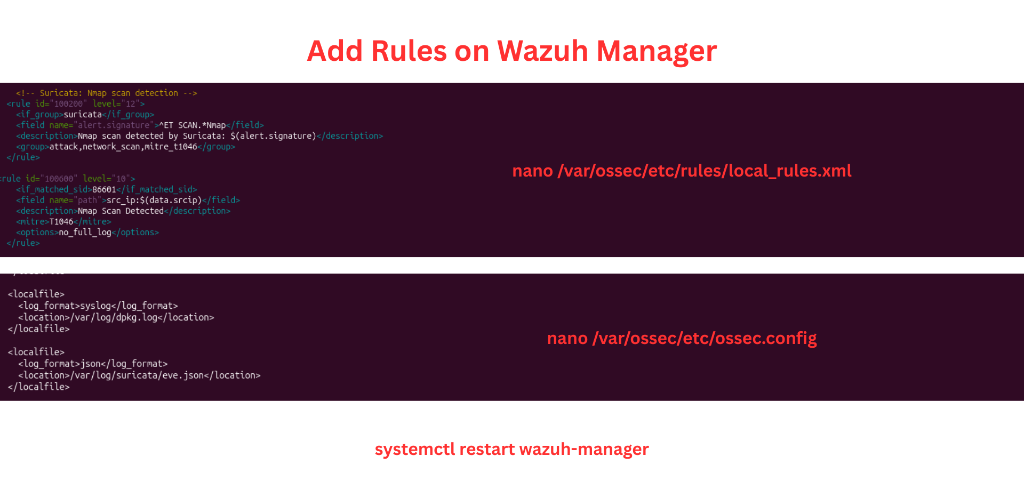
Step 3: Simulating an Attack (The Fun Part!)
It’s time to see our creation in action! We are going to simulate an attack by executing a stealth SYN scan (-sS) using Nmap against our monitored machine.
From an attacker machine (or your terminal), run the following command, replacing <victim_ip> with your target’s actual IP address:
nmap -sS <victim_ip>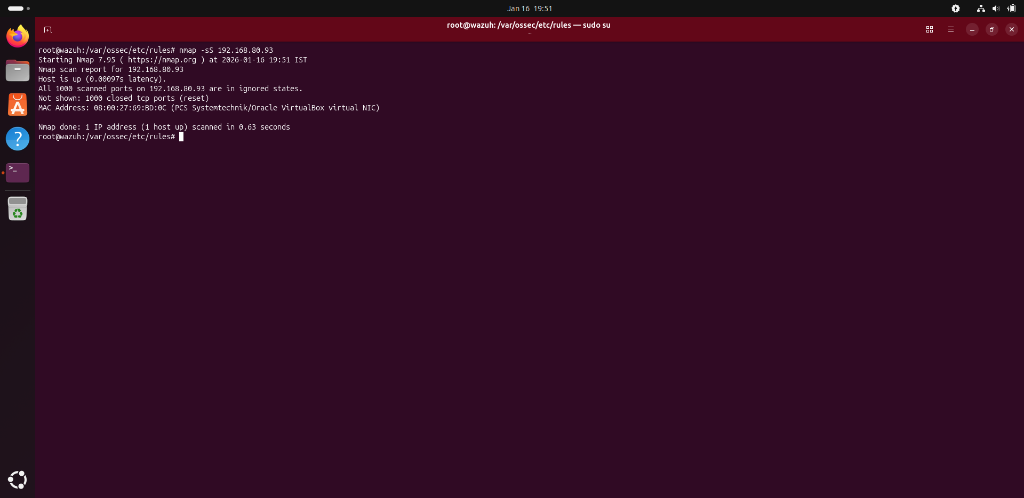
During this scan, Nmap transmits TCP SYN packets across common ports to discover open listening services. Suricata captures this packet pattern, evaluates it against Emerging Threats (ET) signatures, triggers an alert, and writes the structured JSON event to eve.json. The Wazuh Agent picks it up instantly.
Step 4: Viewing the Alerts in the Wazuh Dashboard
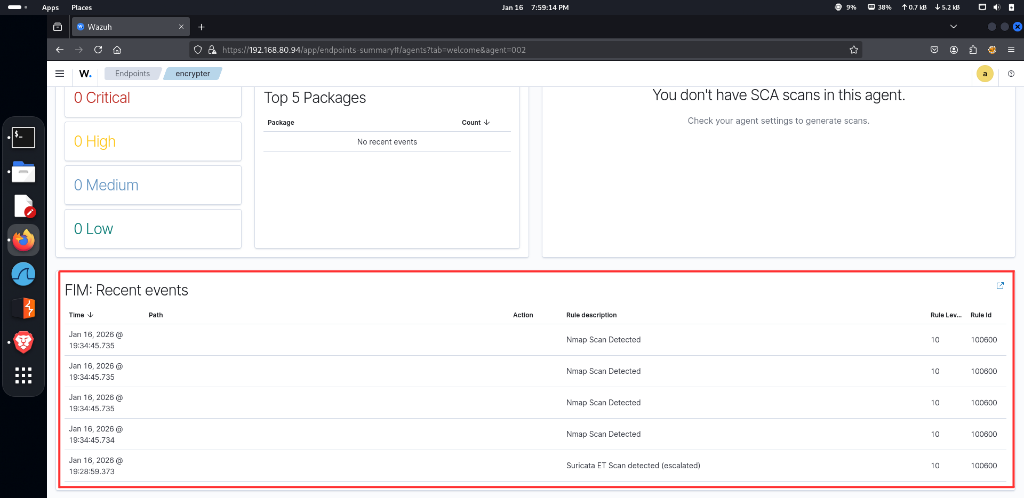
Now, log into your Wazuh Web Dashboard and navigate to the Security Events module (or Endpoints Summary for your agent).
Because of the rules we configured, you will immediately see high-level alerts popping up. The dashboard will show a “Nmap Scan Detected” event with Rule ID 100600 (or 100200). Suricata detected the scan, generated the log, and the Wazuh Agent pushed it to the SIEM in real-time!
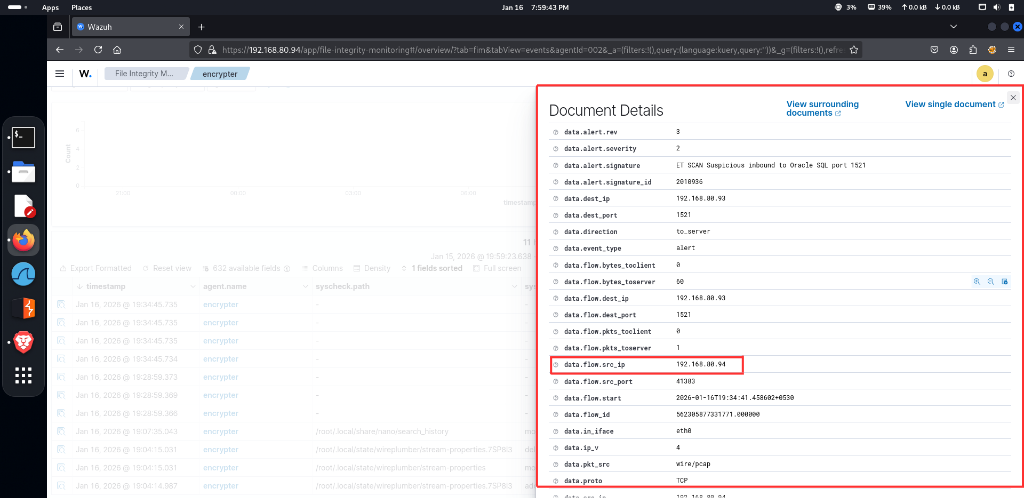
Deep Forensic Analysis: Document Details
You can click on these events to inspect the Document Details panel. This detailed view provides crucial forensic evidence for a SOC analyst:
- Source IP (
data.flow.src_ip): Pinpoints the exact IP address of the attacker (192.168.80.94). - Destination Port (
data.dest_port): Identifies targeted ports probed during the scan. - Alert Signature (
data.alert.signature): Displays the specific Suricata detection rule triggered (e.g.,"ET SCAN Suspicious inbound to Oracle SQL port 1521"). - Protocol & Interfaces: Provides raw network packet attributes (
TCP,eth0) and flow metrics.
Conclusion
Congratulations! You have successfully integrated Suricata IDS with Wazuh SIEM. This setup is incredibly powerful and reflects architectures utilized by real-world Security Operations Centers (SOCs) to monitor network traffic, detect reconnaissance scans, and stop intrusions before adversaries can gain a foothold.
Cybersecurity is all about visibility — you can’t protect what you can’t see. By combining Wazuh and Suricata, you give yourself a pair of x-ray glasses for your network.
If you found this guide helpful or want to dive deeper into the code, check out the complete project on my GitHub:
🔗 jaseervk / Network-Intrusion-Detection-using-Suricata-IDS-Wazuh-SIEM-
Feel free to star ⭐ the repository if it helps you out, or leave a comment below if you have any questions!
If you love my content and want to support my cybersecurity journey, consider buying me a coffee!
Other Digital Presences
- Buy Me a Coffee: buymeacoffee.com/jaseervk
- GitHub: github.com/jaseervk
- Portfolio: www.jaseervk.com
- Blog: blog.jaseervk.com
- LinkedIn: linkedin.com/in/jaseer-vk-
- Medium: https://medium.com/@jaseervk321